 ace
Self-Supervised One-Class Tabular Deep Learning for Intrusion Detection in Artificial Intelligence of Things Systems
The emergence of the artificial intelligence of things (AIoT) has led to increasingly sophisticated cyberattacks. For many of these threats, labeled training data are scarce or unavailable, which increases the need for label-free intrusion detection systems. To address this issue, this study proposes a self-supervised one-class TabNet framework, termed SS-OC-TabNet, for intrusion detection in tabular network traffic. The framework combines self-supervised representation learning and one-class compactness learnin…

In brief
Researchers built SS-OC-TabNet, an intrusion detection framework for tabular network traffic in AI-enabled Internet of Things settings. It first learns the structure of normal traffic from unlabeled data by reconstructing masked features, then tightens the representation of normal traffic so deviations stand out as anomalies.
The work matters because labeled attack data are often scarce for new threats, so detectors that need no labels could help defend connected devices. The evidence is a published model evaluation, and the reported results show promise rather than proven field deployment.
Main points
- The framework uses a two-stage process: masked-feature reconstruction followed by a hypersphere compactness objective.
- TabNet serves as the backbone, enabling sequential feature selection and interpretability of which traffic features drive decisions.
- It was evaluated on NSL-KDD and compared with related works on ToN-IoT.
- The reported result is 93.20% accuracy and a 2.13% false alarm rate.
- The authors say its compact, low-complexity design supports energy-efficient deployment on resource-constrained devices.
The gain
A two-stage self-supervised one-class model learns normal network traffic without labeled attacks and flags anomalies, reaching 93.20% accuracy with a 2.13% false alarm rate in the authors' evaluation.
The rundown
The study starts from the rise of sophisticated cyberattacks linked to the artificial intelligence of things and the shortage of labeled training data for many of those threats, which motivates label-free detection.
The method trains on normal traffic only. Masked-feature reconstruction teaches the model the feature structure of normal behavior, and a hypersphere objective then makes latent representations of normal traffic more compact for anomaly detection.
Interpretability results indicate which network traffic features influenced the model's decisions. The authors conclude the model is a viable label-free tool for AIoT environments, with its low computational complexity supporting deployment where resources are limited.
Sources
- Peer-reviewedJournal of Computational and Cognitive Engineering2026-10-15

It’s going to take more than an email to a public inbox to protect Australians from potential AI doom | Tom McIlroy
The Guardian
OpenAI says agents leaked 53 images from ChatGPT users in latest example of rogue activity
The Guardian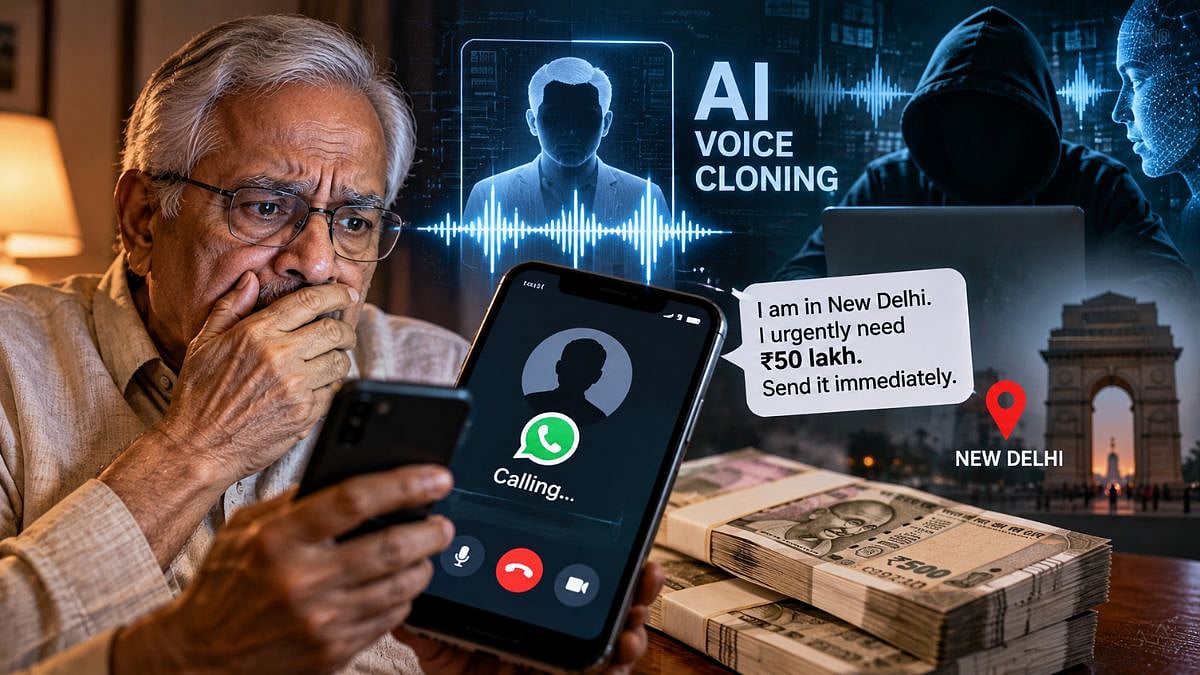
Mumbai Cyber Fraud: 69-Year-Old Senior Citizen Loses ₹50 Lakh In AI Voice-Cloning Scam
Free Press Journal
The debate